For a decade, KYC in iGaming meant a queue. A player registered, played, and then hit a withdrawal request that triggered a manual document review, a multi-day delay and—too often—an abandoned account. That model is now commercially and regulatorily obsolete. Regulators across the MGA, UKGC and newly licensed Latin American markets require identity assurance before material activity, and players have been trained by fintech to expect account opening in seconds. The result is a genuine engineering conflict: verify earlier, verify harder, and still convert. Player identity verification in 2026 is therefore an architecture problem, and the architecture must reconcile two opposing pressures with the same pipeline. This is the companion piece to our analysis of real-time AML 2.0: KYC establishes who the player is, AML monitors what they do—and both must run on shared, low-latency infrastructure.
Why KYC 2.0 Is an Architecture Decision, Not a Vendor Purchase
Most operators do not have a KYC strategy; they have a KYC vendor list. A document scanner from one supplier, a liveness SDK from another, a device-fingerprinting library from a third, a sanctions-screening feed from a fourth, and a manual review queue stitched between them by an operations team. Each component is defensible in isolation. The system as a whole is not, for three reasons.
- Signal fragmentation. The device fingerprint knows the player is on a rooted Android emulator. The document check knows the ID matches. The behavioral layer knows the session rhythm looks scripted. No single vendor sees all three, so nobody flags the combination—and the fraud ring walks through the gaps between systems.
- Decision latency compounding. Serialized calls to four vendors turn a 900-millisecond target into four to six seconds of registration friction. Every additional second at this stage is measured in lost first-time deposits.
- Audit opacity. When a regulator asks why a specific account was onboarded without enhanced checks, “each vendor returned a pass” is not an answer. The operator must be able to produce a single, reconstructable decision record with the contributing signals and the policy version that governed it.
KYC 2.0 addresses this by making verification an orchestration layer—a policy engine that calls specialized signal providers in parallel, fuses their outputs into one risk score, executes a graduated decision, and writes an immutable decision record. Vendors become interchangeable components beneath a stable policy layer.
The Four Layers of a Modern Identity Stack
Layer 1: Document Forensics
The foundational layer validates the identity document itself before any question of “does this face match” is asked. Modern forensics runs well beyond OCR: it inspects substrate and print artifacts, checks MRZ and barcode checksums for internal consistency, detects digital splicing and recapture (a photo of a screen, often called a screen-replay attack), and validates the document against the issuing country’s template library. Critically, it should validate that the document type is actually valid for the player’s declared age and residency—a surprising share of fraud attempts use expired or mismatched document classes.
Layer 2: Biometric Liveness and Face Match
This is where the 2026 threat landscape has changed most. Passive liveness—analyzing a single selfie frame for texture, depth cues and moiré patterns—is now table stakes but insufficient on its own. Generative video injection, where an attacker feeds a synthetic face stream directly into the camera API rather than presenting it to a real camera, defeats naive passive checks because there is no “real” scene to analyze. The architectural answer is challenge-response liveness with camera integrity attestation: randomized challenges that are impractical to pre-record, combined with platform-level attestation (Play Integrity, App Attest) that verifies the camera stream originates from genuine hardware rather than an injected virtual camera.
Layer 3: Device, Network and Graph Analysis
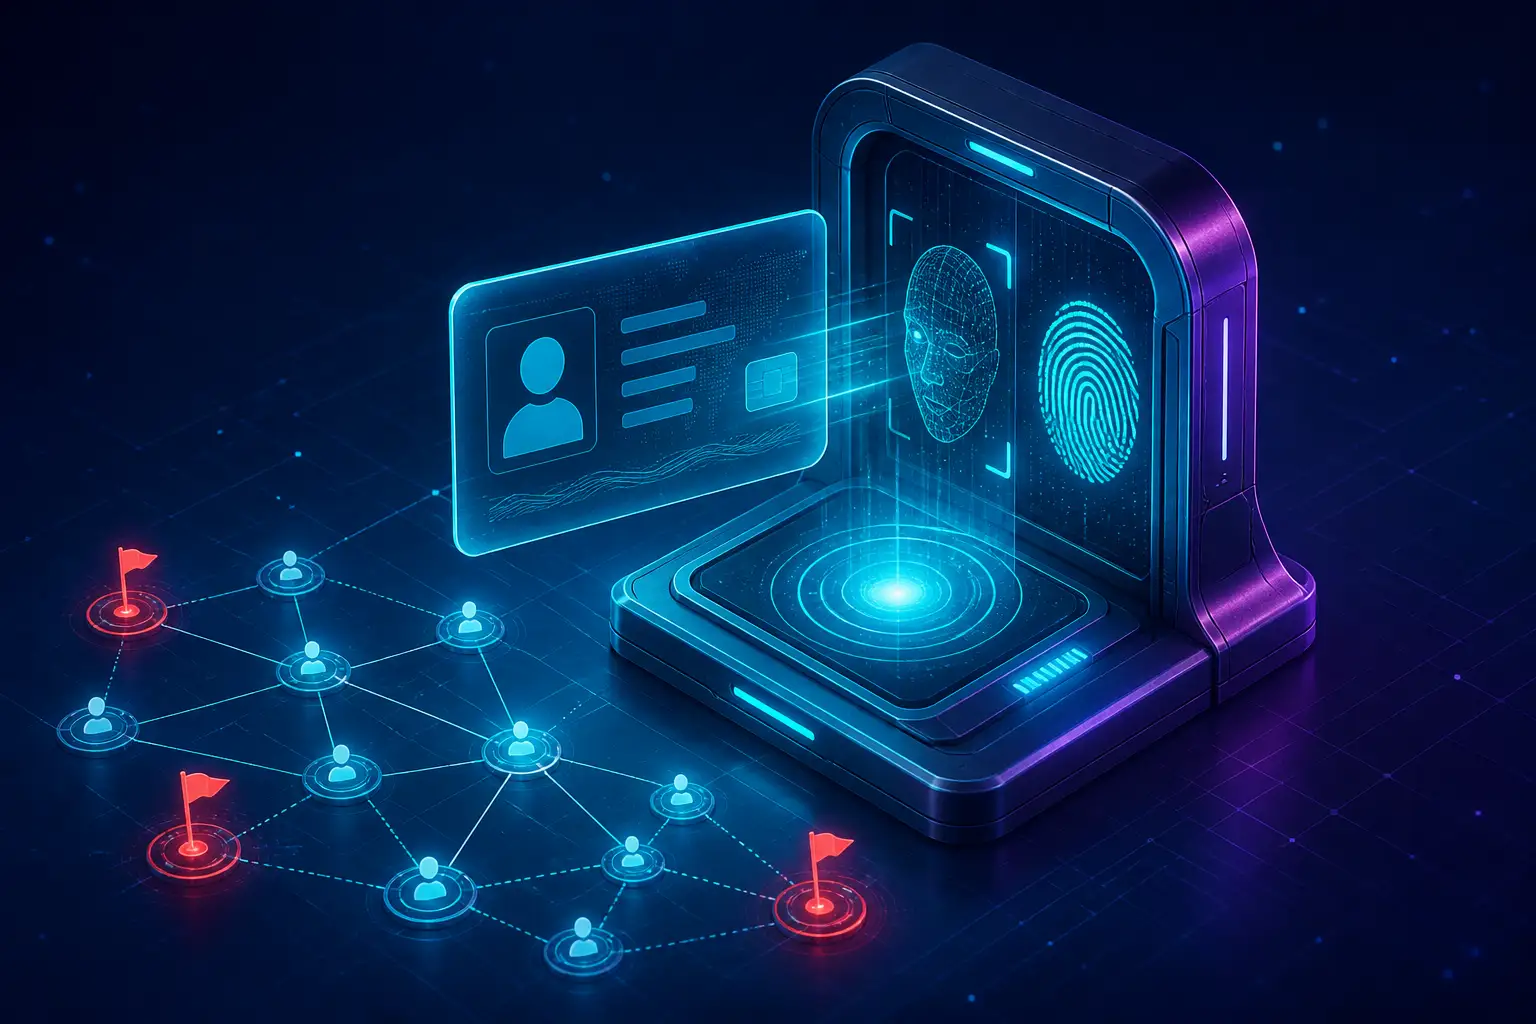
Identity documents are cheap to forge at scale; device and network graphs are not. This layer builds a persistent identity graph from device fingerprints, IP reputation and geolocation, TLS and network characteristics, wallet and payment-instrument reuse, and session-level behavioral signals. Its purpose is to answer a question no single check can: is this new account structurally related to known bad actors or to other accounts that should not be linked?
Layer 4: Risk Orchestration and Decisioning
The orchestration layer owns the policy. It dispatches checks in parallel, applies jurisdiction-specific rulesets, computes a unified risk score, and selects a graduated outcome: pass, pass-with-monitoring, step-up verification, manual review or decline. It also owns the audit trail. In a well-designed stack, this layer is the only component that compliance teams need to reason about when a regulator asks how a decision was made.
Liveness Detection in the Deepfake Era
The economics of identity fraud shifted decisively in 2025–2026. Synthetic identity tooling that once required specialist expertise is now commoditized, and fraud-as-a-service operations sell verified-looking onboarding kits on the same forums where they sell stolen card data. The practical consequence for operators is that any verification step which can be satisfied by a pre-recorded or generated artifact should be assumed to be defeated.
Three design principles follow:
- Prefer challenges that are unknowable in advance. Randomized instruction sequences, on-screen gestures and dynamic depth prompts raise the cost of pre-recorded replay attacks to a level most fraud rings will not pay.
- Attest the capture environment, not just the face. If the platform cannot verify that the camera and sensor pipeline is genuine hardware, liveness analysis is being performed on data the attacker fully controls.
- Treat liveness as a signal, not a verdict. A marginal liveness score combined with a clean device graph should be treated differently from the same score combined with a device cluster that has produced three declined accounts this week. Fusion beats thresholds.
Pass-Rate Optimization Without Regulatory Exposure
Every compliance head faces the same internal tension: fraud and compliance push toward stricter thresholds, while growth and CRM push toward higher pass rates. The resolution is not to lower the bar but to segment the bar. A single global threshold is simultaneously too strict for a genuine 22-year-old on a clean device in a low-risk jurisdiction and too loose for a high-velocity registration cluster on datacenter IPs.
The matrix below illustrates the graduated posture that a mature orchestration layer applies. The bands are directional; actual thresholds must be calibrated against each operator’s own traffic.
| Composite Risk Band | Typical Signal Pattern | Action | Expected Pass Rate (indicative) |
|---|---|---|---|
| Low | Genuine document, clean device attestation, consistent geo, no graph links | Instant pass, standard monitoring | 92 – 97% |
| Moderate | Minor OCR mismatch, VPN use, shared device, first-time payment instrument | Pass with step-up: enhanced selfie or secondary document | 78 – 88% |
| Elevated | Emulator or virtual camera signature, datacenter IP, document template anomaly | Manual review with time-bounded SLA | 45 – 65% |
| High | Graph match to prior confirmed fraud, injection indicators, sanctioned-identity proximity | Decline, log, feed back to graph, consider SAR/STR workflow | under 10% |
The optimization discipline is to move genuine players up the confidence ladder rather than lowering thresholds globally. Two levers do most of the work: (1) step-up rather than decline in the moderate band, so that a legitimate player with a VPN is asked for one additional signal instead of being rejected; and (2) fast feedback into the graph, so that confirmed-fraud outcomes immediately enrich the device and network relationships that drive the elevated and high bands. A stack that learns from its own declines will improve pass rates and fraud precision simultaneously.
Device-Graph Fraud Ring Detection in Practice
Fraud in iGaming is overwhelmingly organized, not individual. A single actor rarely matters; a ring of forty accounts exploiting a bonus scheme does. The tool designed for this is the identity graph, and its value is realized through link analysis rather than per-account scoring.
A Case Pattern: The Bonus Ring on a Latin American Operator
Consider a pattern typical of dual-license operators scaling in Brazil and Malta. Registration volume grew sharply over six weeks, and individual account risk scores were, on their own, unremarkable: genuine-looking documents, moderate deposit activity, no sanctions hits. Manual review capacity was consumed by a growing queue, and the fraud team suspected—but could not prove—that a coordinated ring was farming a registration bonus and a first-deposit incentive.
The graph told the story that per-account scoring could not. Clustering the accounts by device fingerprint, TLS characteristics and payment-instrument reuse revealed a dense component of roughly 230 accounts sharing a small set of device families, three mobile carriers, and an unusually high overlap in crypto deposit addresses. Each individual account looked acceptable; the structure looked industrial. The operator had been solving a per-account problem while facing a network problem.
The remediation pattern that worked was layered. First, the connected component was flagged and routed to enhanced review rather than blanket-declined, because some legitimate players shared carriers with the cluster. Second, the orchestration layer was retuned so that graph density rather than individual score became the dominant signal for this market. Third, the operator reduced the exploit’s profitability by adjusting the qualifying conditions for the affected promotion—addressing the incentive rather than only the accounts.
The measurable outcomes over the following quarter were directionally consistent with industry experience: bonus-related abuse losses fell sharply, the manual review queue shrank because low-risk accounts were auto-passed with more confidence, and the fraud team shifted from queue-clearing to graph investigation. The important architectural point is that none of this required a new vendor. It required the operator to route device, payment and network signals into one place where they could be analyzed as a graph.
Integration With AML 2.0 and the Compliance Stack
Identity verification does not end at onboarding. The same identity signals that approved the account must remain live so that transaction monitoring can act on them. This is the connective tissue between KYC 2.0 and AML 2.0: an onboarding risk band that feeds the transaction-monitoring threshold logic, a device graph that enriches suspicious-activity narratives, and a decision ledger that gives investigators a single timeline of identity, payments and gameplay.
For operators pursuing a single technical backbone, this convergence is a deliberate design goal at DYG Games. Our platform architecture assumes that identity, transaction monitoring and responsible gaming all observe the same event stream, which eliminates the reconciliation work that otherwise consumes compliance engineering capacity. The same principle underpins our approach to stablecoin and multi-rail settlement, where identity assurance directly affects withdrawal risk.
Frequently Asked Questions
Does KYC 2.0 mean we must verify every player before they can play for free?
Not necessarily, but the direction of travel is clear. Many regulators now permit low-friction play while requiring verified identity before deposit, before bonus participation, or within a defined window after registration—often 72 hours to 30 days depending on the jurisdiction. The architectural requirement is that the orchestration layer can enforce whichever policy applies per market, and that unverified accounts are structurally prevented from reaching the activities the regime restricts. A single hard-coded rule will not survive multi-market operation.
How much does stronger liveness detection cost us in conversion?
If implemented as a replacement for a weaker passive check, challenge-response liveness adds a few seconds and typically reduces instant pass rates by a low single-digit percentage in clean traffic—the loss is concentrated in marginal cases that frequently warrant review anyway. The net effect on first-time-deposit value is usually positive once you account for the reduction in fraudulent accounts and chargebacks. The critical implementation choice is to reserve step-up challenges for elevated signals rather than applying them universally.
Can we run KYC entirely on the client, or must it be server-side?
Hybrid is the practical answer. Capture, quality guidance and initial liveness challenge can run on-device for latency and privacy reasons. Document forensics, face match and graph lookups should be server-side so that policy, evidence and audit trails remain under operator control and cannot be manipulated by a compromised client. On-device inference is best treated as a performance optimization, never as the authoritative decision.
What do regulators actually expect us to be able to demonstrate?
Three things: that a documented policy existed at the time of the decision, that the signals used are consistent with that policy, and that the outcome is reconstructable. In practice this means versioned policy definitions, a tamper-evident decision ledger with contributing signals, and retention schedules aligned to local data-protection law. Documentation is where most operators fail audits—not detection capability.
How does this differ from the AML controls we already have?
KYC answers “is this person who they claim to be, and are they permitted to hold an account?” AML answers “is this person’s activity consistent with their profile, and does it warrant reporting?” They share infrastructure—the identity graph, the risk score, the event stream—but they operate on different timescales. KYC is a decision at a point in time; AML is continuous monitoring. A well-architected stack runs both on the same pipeline rather than duplicating data collection.
What is the role of self-exclusion and identity in player protection?
Identity is what makes self-exclusion enforceable and portable. If a self-excluded individual can re-register with a new email address and an unchanged device, the protection is nominal. Matching registration attempts against the identity graph—device, payment instrument, document biometrics—is what turns a self-exclusion register into an actual barrier. This is one of the clearest examples where fraud prevention and player protection share the same underlying capability.
How long should we retain verification evidence?
Retention is jurisdiction-specific and increasingly contested. AML regimes in mature markets typically require five years, some licenses extend to ten, and data-protection law simultaneously demands that biometric data be minimized and retained no longer than necessary. The pragmatic architecture stores the decision record and the risk rationale for the full regulatory period while minimizing raw biometric artifacts and applying aggressive deletion to intermediate processing data. Legal review per market is mandatory; a single global retention policy is a compliance risk.
Conclusion: One Identity Layer, Two Mandates
Player identity verification in 2026 is not a gate to be staffed and a queue to be cleared. It is a real-time decision system that must simultaneously serve growth, fraud and regulatory obligations from a single event stream. Operators who build it as an orchestration layer—documents, biometrics, device graphs and policy in one place—gain pass rates and fraud precision at the same time. Operators who keep buying point solutions will keep finding rings in the gaps between them.
DYG Games builds identity, transaction monitoring and player protection into the same platform backbone, so that a verified player is a verified player across every jurisdiction and every game in the catalog. If your roadmap includes a new market or a new payment rail this year, the identity layer is the right place to start the architecture conversation.
Request a technical walkthrough of our identity orchestration and fraud-graph integration model, and we will map it against the regulatory requirements of the markets on your license roadmap.